
Compliance
Experts who attack.
An engine that keeps watch.
Continuous monitoring of your attack surface with Kynapt, our own engine: it detects exposed assets and newly published vulnerabilities, and every finding goes through a certified pentester before it reaches you. No reports that go stale.
Certified.
Ethical.
Rigorous.
Trusted.
Our team is certified in offensive security
Hands-on certifications held by Kamaya Secure consultants, earned by compromising real systems under exam conditions.
About Kamaya Secure
We are a Peruvian consultancy specialized in offensive security. Kynapt, our continuous monitoring engine, works all year round: it discovers your exposed assets, detects newly published vulnerabilities and cross-checks the versions of your technology. Certified pentesters validate every finding before it reaches your team, and you see it in your portal in real time.
We combine certified technical expertise with first-hand knowledge of Peruvian regulation and operating context, so every finding translates into concrete decisions.
We work with clear rules, formal authorization and full confidentiality: our clients’ trust is the foundation of everything we do.
Certified pentesters
Hands-on certifications such as OSCP, OSCP+, CRTP, eCPPT, eWPTX, eWPT, eMAPT and eJPT, earned by compromising real systems under exam conditions.
Traceable methodology
Findings with reproducible evidence, mapped to MITRE ATT&CK: what to fix, why, and in what order.
Local presence
From Lima, in your language and time zone, with on-site work and deliverables aligned with SBS and Law No. 29733.
Reports for two audiences
An executive summary for leadership and a technical report for IT, prioritized by business impact.
Our team
The team that attacks to protect
Pentesters, researchers and engineers who design, run and validate every assessment and every Kynapt finding.
-

Alejandro Manuel Vega Vásquez
Managing Partner · Head of Offensive Security
Managing partner at Kamaya Secure and head of offensive security. He leads the technical relationship with clients in mining, banking and the public sector, aligning every pentest and Red Team exercise with the business. Telecommunications Engineer (UNI).
-

-

Paulo Puicón Gallardo
Project Director
As project director, he coordinates the planning and execution of every assessment, from scoping to the delivery of results. He is the client’s point of contact throughout the engagement and oversees timelines and the quality of deliverables.
-

Jesús Arturo Espinoza Soto
Senior Penetration Tester · Associate Consultant
Penetration tester with over 7 years of experience in web, mobile and infrastructure assessments, recognized in responsible disclosure programs. Certified OSCP, CEH, eCPPTv2, CREST CPSA and Burp Suite Certified Practitioner. Master’s in Cybersecurity.
Kynapt platform
Always on. Always validated.
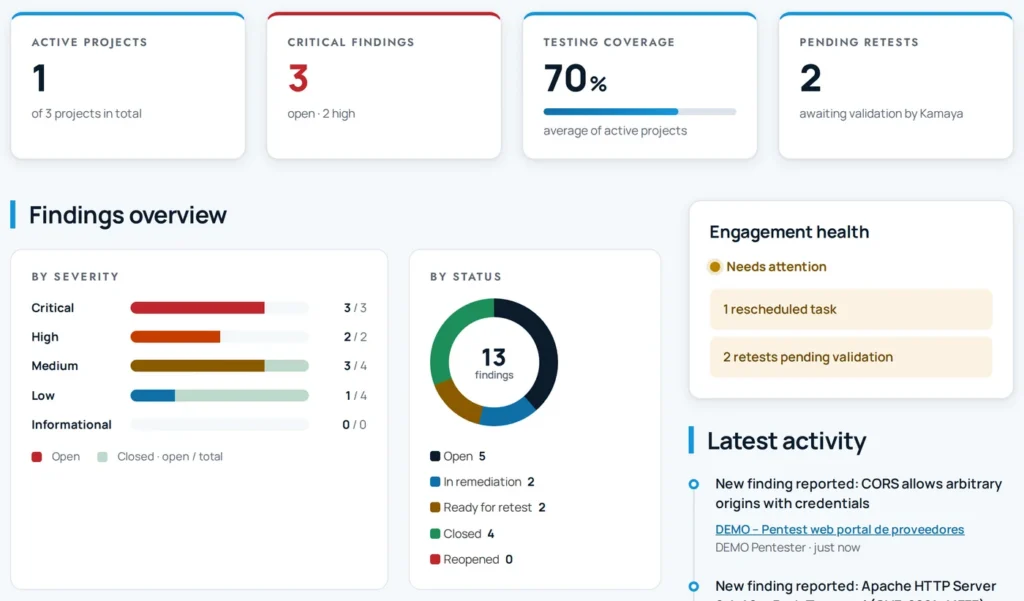
Kynapt watches your attack surface between engagements: it discovers what you expose, retests it when a new vulnerability is published and only delivers what a certified pentester confirmed. All of it, in your client portal.
01
Attack surface radar
Keep an up-to-date inventory of what your organization exposes to the internet, without relying on spreadsheets.
- Discovers subdomains, web services, APIs, ports and technologies from the domains and IP ranges you approved.
- Classifies every asset by type and criticality: remote access, admin panels and sensitive services first.
- Nothing is tested without authorization: every new asset is reviewed by a pentester before it enters monitoring.
- Your portal shows what is being monitored and when it was last checked.

02
Validation engine
Recurring tests on your authorized assets, and a human filter before anything reaches your team.
- Scheduled scans (daily, weekly or monthly) or on demand, with rate limiting so your operations are not affected.
- Detects vulnerabilities with a published CVE, insecure configurations, exposed services and default credentials.
- Triage removes duplicates and prioritizes; every critical or high finding always goes to a pentester.
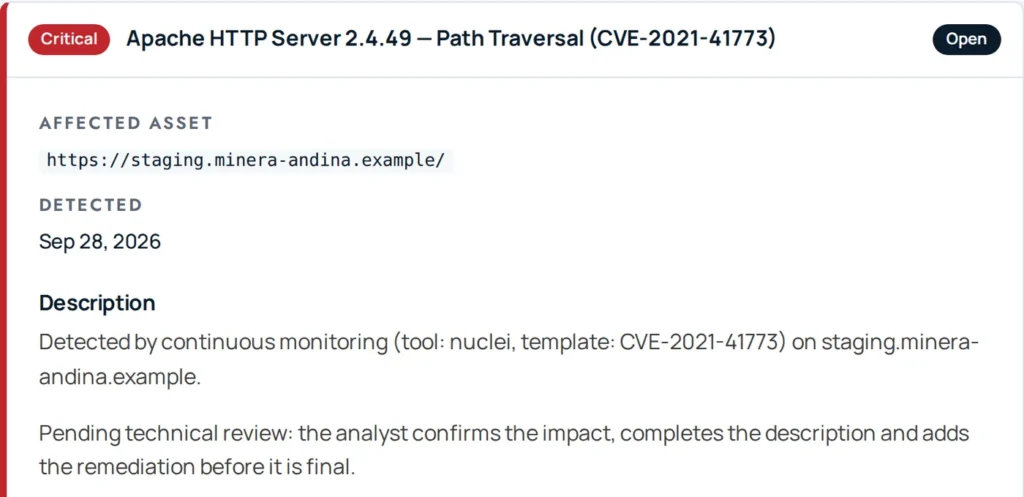
- By default, only what a certified pentester confirmed is published to your portal.
03
Remediation hub
From finding to verified fix, with traceability for your team and your auditors.
- Findings with severity, affected asset and recommendation, visible as soon as they are published.
- Your team records the fix and requests a retest; a pentester verifies it and closes the finding.
- Alerts by email, Slack or Jira, without exposing finding details outside the portal.
- Versioned reports and documents, with an integrity check on every download.
Explore our cyber security capabilities
Ten services covering the full cycle (anticipate, withstand and respond), backed by Kynapt, our continuous monitoring engine. Every engagement is tailored to your organization’s maturity, industry and regulatory obligations.
Red Team & Ethical Hacking
Human-led adversary exercises that test whether your organization detects and contains a real attack, with tactics mapped to MITRE ATT&CK.
- Automation
- Between exercises, Kynapt keeps the map of your exposed attack surface up to date, so every campaign starts from what an attacker would see today.
- Human validation
- Certified operators design the attack chain and evasion techniques, and your portal shows what was tested and what your team detected.
Penetration Testing
Manual testing of web applications, APIs, mobile apps, infrastructure and cloud that goes where a scanner can’t.
- Automation
- Kynapt, our continuous monitoring engine, discovers your exposed assets, identifies technologies and versions, and retests them whenever a vulnerability that affects them is published.
- Human validation
- Certified pentesters (OSCP, OSCP+, CRTP, eCPPT, eWPTX and more) manually exploit what Kynapt flags and look for what no tool can see. You follow progress in your portal.
Source Code Review
We find vulnerabilities in your code before they reach production, in any language.
- Automation
- Automated analysis scans your entire codebase and its open-source dependencies for insecure patterns and known CVEs.
- Human validation
- Our reviewers manually validate critical logic (authentication, authorization and data handling) and discard false positives.
OT/ICS Security
We assess your industrial control systems (IT/OT segmentation, IEC 62443 and NERC CIP) without stopping operations.
- Automation
- Kynapt watches the internet-facing edge of your industrial network. Inside the OT network we use passive methods only, never active scanning.
- Human validation
- Our specialists validate every test in a lab before touching a production environment, and you see the status in your portal.
Social Engineering & Awareness
Controlled phishing, vishing and malicious QR campaigns that measure the human factor and turn it into a line of defense.
- Human validation
- Specialists design realistic scenarios for your industry and turn the results into concrete training.
Bug Bounty & Vulnerability Disclosure
We design and run your responsible disclosure and bug bounty program with our own community of researchers.
- Automation
- Every report is checked against your program’s authorized scope, so out-of-scope submissions don’t take up your team’s time.
- Human validation
- Our pentesters reproduce every report and confirm its severity before it reaches you.
Incident Response & Forensics
We contain the incident, identify the root cause and guide recovery following NIST SP 800-61.
- Automation
- If your organization uses Kynapt, the asset inventory and previous findings are already in the portal, which shortens the initial analysis.
- Human validation
- Our team leads containment and preserves evidence with chain of custody.
Compliance & Risk Management
We prepare your organization for ISO 27001, SBS Resolution No. 504-2021, PCI DSS and Law No. 29733, with controls that work in practice.
- Automation
- The history of Kynapt scans, findings and retests in the portal serves as documented evidence of your vulnerability management cycle.
- Human validation
- Our consultants prove that each control actually works, not just that it is written in a policy.
CISO as a Service
Outsourced security leadership: strategy, roadmap and board reporting, without the cost of a full-time executive.
- Automation
- The portal gives your board up-to-date indicators: open findings by severity, pending retests and the progress of each engagement.
- Human validation
- Your outsourced CISO prioritizes risks according to your business and drives execution with our technical team.
Zero Trust
Consulting to design and adopt a zero trust model: identity, segmentation and continuous verification.
- Automation
- Kynapt checks from the outside that no services remain exposed beyond the perimeter your Zero Trust architecture should close.
- Human validation
- Our pentesters attack the implementation to confirm that segmentation and access controls hold up in practice.
Sectors where continuity is non-negotiable
Every industry has its own attack surface, regulators and timelines. We tailor the scope and language of each engagement to your operational reality.
Mining
Remote operations, critical OT assets and extended supply chains. We protect production continuity.
Banking & Fintech
SBS and PCI DSS requirements, digital fraud and exposed APIs. We assess your risk through an attacker’s eyes.
Government
Digital citizen services, personal data and legacy systems. We help public entities protect them.
Latest insights
Compliance
SBS Resolution No. 504-2021: what it means for your cybersecurity program
Peru’s SBS regulation on information security and cybersecurity requires a management system backed by evidence that controls work. What it requires, who it applies to and where technical testing fits.
OT/ICS
IT/OT segmentation in mining: where to start
The convergence of corporate and industrial networks opens paths an attacker can exploit. A six-step roadmap to bring order with IEC 62443 without stopping operations.
Red Team
Red Team or pentest: which one your organization needs, and when
Both simulate attacks, but they answer different questions. How to choose between a penetration test and a Red Team exercise based on your organization’s maturity.
Attackers don’t wait. Get ahead with Kamaya Secure.
Knowing in time how your organization could be attacked is the most efficient way to protect your operations, your reputation and your customers.
Talk to a specialist: together we agree on scope, rules of engagement and deliverables before we start.